

Cyber resilience bill: what you need to know now
3 minute read
Jonny Scott
October 20th, 2025
In response to increasing cyber threats on the UK public sector, the government has introduced the Cyber Security and Resilience Bill, a piece of legislation designed to strengthen our national defences. But what does this mean for your organisation? Jonny Scott, Head of Cyber Advisory at Phoenix, takes a look…
“The Cyber Resilience Bill, announced in the 2024 King’s Speech and detailed in April 2025, is the UK’s most significant cyber legislation update since the Network and Information Systems (NIS) Regulations of 2018. It’s a direct response to the escalating number of threats, where hospitals, universities, and government departments have become prime targets for cyber criminals and hostile state actors.
What’s changing?
The Bill expands the scope of cyber regulation to include a broader range of digital services and supply chains. Managed IT service providers, cloud platforms, and even smaller third-party vendors may now fall under regulatory scrutiny. This shift reflects the reality that attackers increasingly exploit supply chain vulnerabilities to infiltrate critical infrastructure.
Key measures include:
- Enhanced incident response protocols: organisations must report cyber incidents to the National Cyber Security Centre (NCSC) more frequently and transparently
- Stronger supply chain risk management: expect mandatory third-party risk assessments and tighter controls on vendor relationships
- Designation of ‘Critical Suppliers’: regulators can now classify key suppliers as critical, bringing them into scope for compliance
Why this matters to you
If your organisation delivers or supports essential public services, you’re likely in scope. That includes local authorities, NHS trusts, universities providing IT infrastructure, managed services, or cyber security solutions. The Bill isn’t just about compliance, it’s about resilience. It’s about ensuring that when/ if a cyber incident occurs, your organisation can respond swiftly, recover effectively, and continue delivering vital services.
We’re here to help
We’ve already begun helping public sector organisations assess their readiness through the NCSC’s Cyber Assessment Framework (CAF).
We’re also seeing increased interest in Zero Trust architectures, information security strategies, and managed SOC services, all of which align with the Bill’s emphasis on proactive defence and continuous improvement.
Next steps for your organisation
- Assess: determine whether your organisation or suppliers fall under the new framework
- Conduct a cyber resilience audit: use the NCSC CAF or similar frameworks to evaluate your current posture
- Engage your supply chain: talk to us about how to assess and secure your supply chain with supply chain risk management
- Plan for incident reporting: establish clear protocols for notifying the NCSC and other regulators and align existing playbooks to include clear, defined processes
Ready to strengthen your cyber resilience?
Whether you’re navigating new compliance requirements or building a proactive defence strategy, Phoenix is here to help. Our Cyber Security Specialists work closely with public sector organisations to assess risk, secure supply chains, and implement robust solutions that align with the Cyber Resilience Bill.
Contact us
About the author
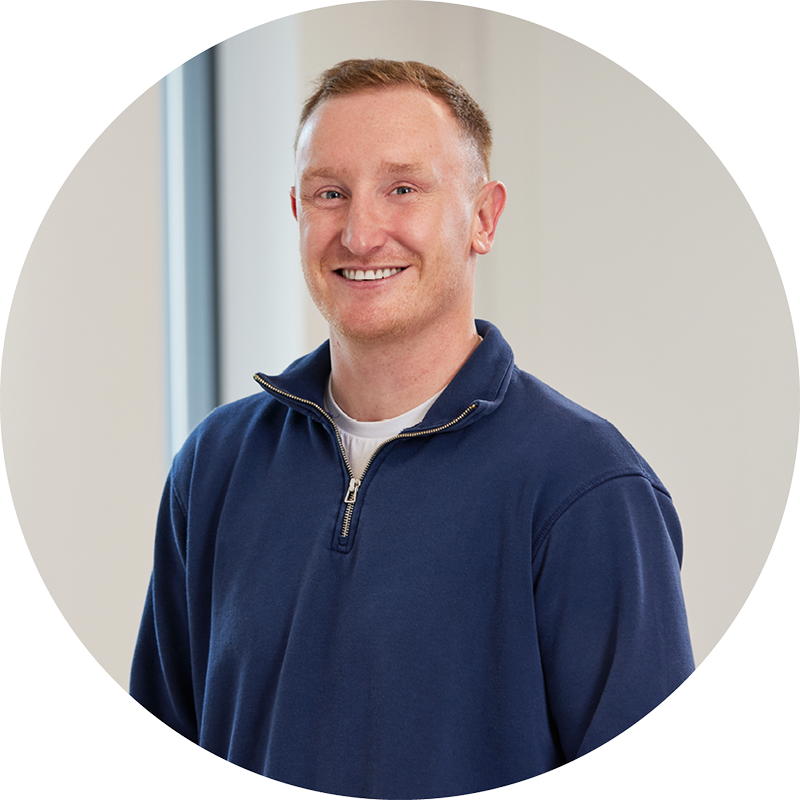
Jonny Scott, Head of Cyber Advisory.
Beginning his career in IT at 17, Jonny first built a strong foundation in Corporate Sales, where he developed a deep understanding of customer needs and the commercial drivers behind technology adoption. Even in these early years, long before cyber security became the priority it is today, Jonny was drawn to the challenge and importance of helping organisations protect their people and data. This ambition guided his move into more strategic roles within business development, building out a security focused strategy for Phoenix.