

Phoenix signs the Government Cyber Resilience Pledge
3 minute read
Phoenix Software
August 4th, 2026
Phoenix has signed the Government Cyber Resilience Pledge, run by DSIT and the NCSC. The pledge commits us to board-level cyber governance, sign-up to Early Warning, and Cyber Essentials checks across our supply chain.
What is the Government Cyber Resilience Pledge?
The government issued a ministerial letter on 13th October 2025, asking organisations to strengthen their cyber resilience. DSIT and the NCSC launched this pledge in response.
The pledge is voluntary. Signatories commit to three core actions, plus a small number of supporting steps. Phoenix has signed up to all of them.
What Phoenix has committed to
1. Make cyber a Board responsibility
- Implement every action in the NCSC’s Cyber Governance Code of Practice
- Every board member completes the NCSC’s Cyber Governance Training within three months, then annually
2. Sign up to Early Warning
- Register for the NCSC’s Early Warning service within one month of signing
3. Require Cyber Essentials across our supply chain
- Register with the Cyber Essentials Supplier Check Tool within two months
- Audit Cyber Essentials coverage across our supply chain and present the findings to the Board
- Take a risk-based approach, backed by other assurance where Cyber Essentials isn’t required
Wider commitments
Beyond the three core actions, we’re also committing to:
- Encourage our suppliers to understand and manage their own cyber risks
- Publish our signed declaration on our website, with an annual public update on our progress
Where can you find more information?
See the Cyber Governance Code of Practice and the NCSC’s Early Warning service for more detail.
View the pledge here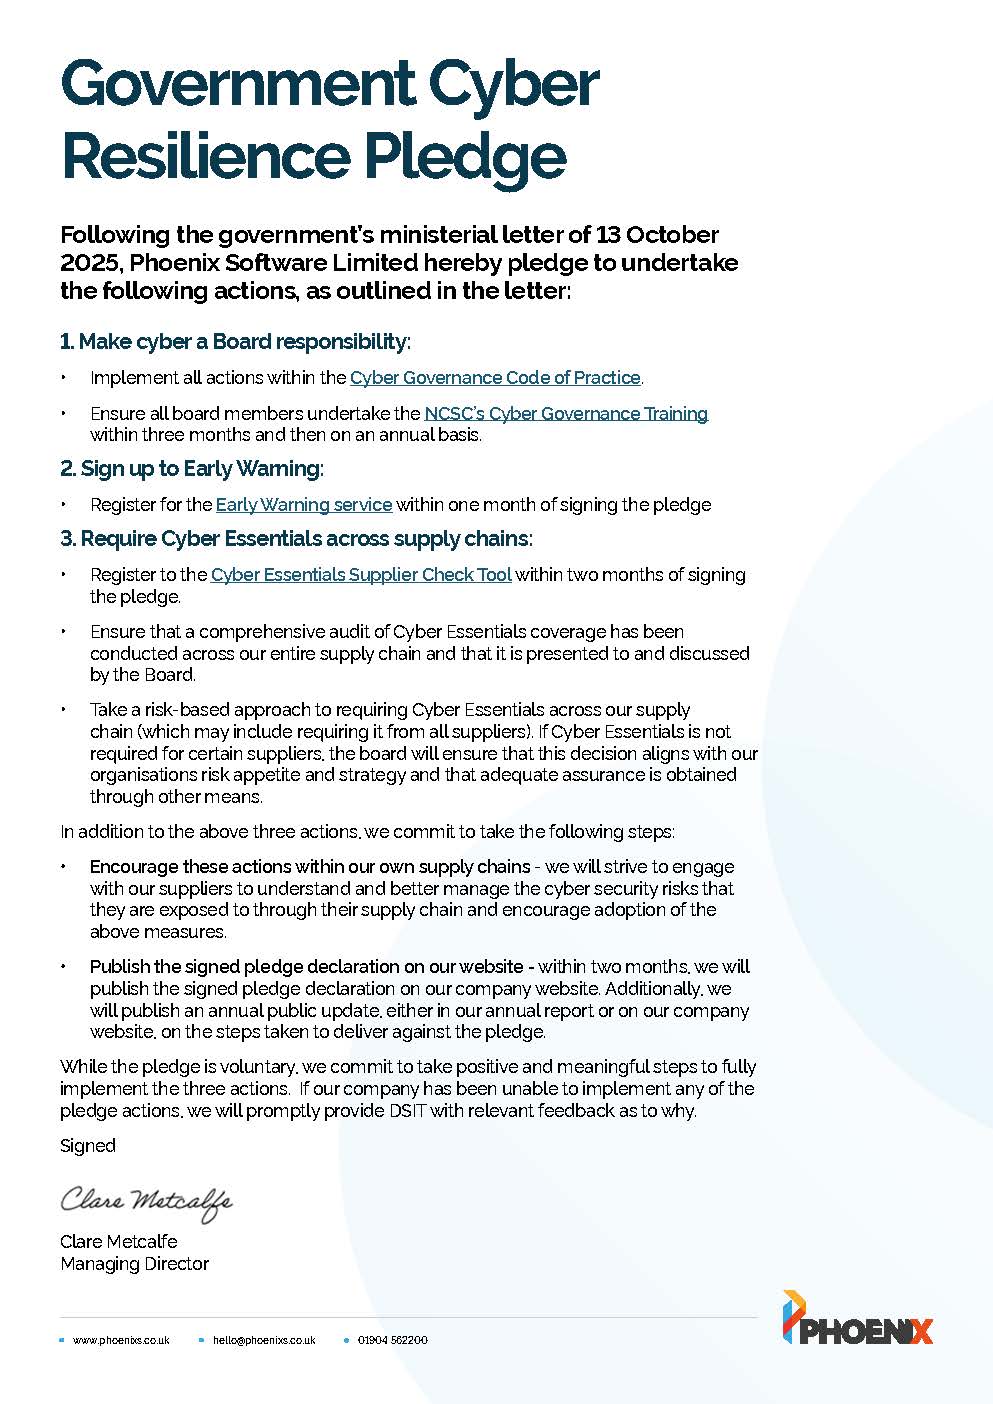
About the author
Phoenix Software
Phoenix enables digital transformation in the workplace, empowering UK public sector organisations to innovate and transform with cloud and hybrid infrastructures, data, AI, security, and collaboration tools. By understanding its customers’ goals, Phoenix delivers outcome–focused IT solutions that make a difference to the lives of employees, service users, and communities.
Follow Phoenix Software on LinkedIn.