
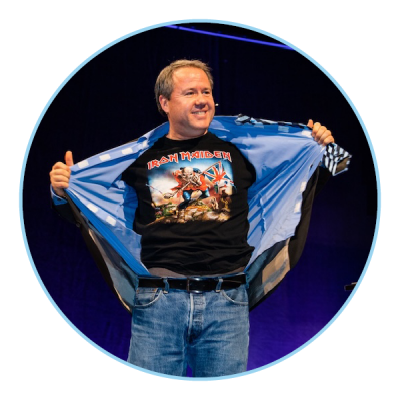
Keynote speaker: Tobias Schroedel
Live Comedy Hacker and Cybersecurity Expert, Tobias Schroedel is opening Public Sector Security Live with a truly unique session. Tobias combines comedy and cyber security expertise to deliver sessions that are more than just thought-provoking, they’re memorable.
He specialises in demonstrating how attackers get in: the password that falls in seconds, the phone number that isn’t what your screen says it is, and the video call where the person giving instructions isn’t real.
A full day, shaped around your sector.
*The agenda is subject to change.
Doors open on the day at 9am. There’ll be drinks and food available once you’ve registered and time to network on our networking floor.
Live Comedy Hacker and Cybersecurity Expert, Tobias Schroedel is opening Public Sector Security Live with a truly unique session. Tobias combines comedy and cyber security expertise to deliver sessions that are more than just thought-provoking, they’re memorable.
He specialises in demonstrating how attackers get in: the password that falls in seconds, the phone number that isn’t what your screen says it is, and the video call where the person giving instructions isn’t real.
Room one: Knowing who is in your supply chain
This session looks at how to build a true picture of who has access to your data and systems, what to ask for during procurement, and where to focus when you can’t access everyone. We’ll cover what good supplier assurance looks like when you have limited leverage and even more limited resource.
Room two: Closing the most common entry point
Compromised credentials remain the way most attackers get in, and identity is now the control that matters most across sprawling estates and hybrid working. This session covers practical identity and access management: MFA that holds up, privileged access, joiners and leavers, and the accounts everyone forgets about.
Room three: When you cannot hire your way out
Public sector security teams are competing for the same scarce skills as everyone else, usually on pay scales that can’t match private sector. This session is about what to do instead. Where managed services help, how to grow capability in the people you already have, and how to structure a small team.
Room One: When paying is not an option
The UK government has set out a targeted ban on ransom payments, alongside new mandatory incident reporting. This session unpacks what the upcoming regime means in practice and, more importantly, what it demands of you before an incident.
Room Two: Understanding shared responsibility in Microsoft 365
Cloud platforms operate on a shared responsibility model, and the line between what the provider protects and what remains yours isn’t always well understood. This session walks through where that line sits for Microsoft 365, why retention policies and recycle bins serve a different purpose to backup, and what that means when you’re facing ransomware, a malicious insider, or a mistaken bulk deletion.
Room Three: Both sides of AI
AI is changing the threat picture and your defences at the same time. This session looks at both. How attackers are using AI to make phishing and social engineering harder to spot. And, where AI is strengthening detection, triage, and response for stretched teams. We’ll also cover the governance that comes with it, including shadow AI.
Take time and break for lunch while getting a chance to network with our partners and specialists.
The topic of this session is TBC. Watch our for our announcements shortly.
Room One: TBC
Room Two: TBC
Room Three: TBC
The topic of this session is TBC. Watch our for our announcements shortly.
Our Head of Cyber Advisory will be chairing a panel discussion to close the day off.
He’ll be joined on stage by a combination of our customers and in-house specialists. More details on this panel will be confirmed shortly.
Before we finish for the day, take one last chance to speak with our partners and specialists.
Headline Sponsors
Gold and Silver Sponsors